


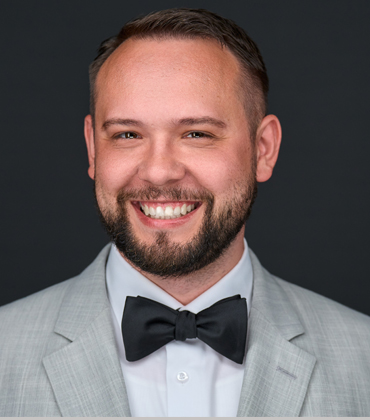
 Piotr Topor, Principal Consultant
Topor Security addresses this gap by reframing cybersecurity as a structured business discipline rather than a collection of technical controls.
"Cybersecurity maturity is not defined by how advanced your tooling is. It's defined by clarity, discipline and consistency," says Piotr Topor, principal consultant.
Framing Cybersecurity through Business Risk
A common challenge organizations face is the disconnect between security activities and business impact. Even with several tools in place, companies remain exposed due to gaps in governance, a lack of accountability and unclear prioritization. Security programs may exist, but without alignment to business objectives, they struggle to deliver meaningful outcomes.
Clients often encounter risks such as ransomware exposure tied to basic control gaps, vendor-related fraud, unmanaged AI adoption and increasing regulatory pressure. These risks are often driven by the absence of structured oversight rather than the lack of tools or technology.
Topor Security begins by aligning cybersecurity with business risk. Leadership discussions focus on identifying disruption scenarios, understanding financial exposure and defining acceptable levels of risk. This approach shifts cybersecurity conversations from technical complexity to business relevance.
By translating security exposure into business language, leadership teams gain clarity and can make informed decisions about priorities, investments and acceptable levels of risk.
Building Structured and Measurable Programs
Topor Security's methodology follows a structured process designed to ensure cybersecurity programs function in practice. Engagements begin with an assessment of organizational maturity against frameworks such as the NIST Cybersecurity Framework.
This assessment identifies control gaps, quantifies risk and establishes prioritized remediation steps. From this baseline, the company builds a program that includes a formal risk register, defined ownership, governance structure, measurable performance indicators and validated incident preparedness.
Technology alignment is also addressed by evaluating existing tools to eliminate redundancy and ensure they support the broader strategy. This ensures that investments contribute to measurable progress and are aligned with organizational priorities.
The result is a cybersecurity program that is not only documented but actively managed, with clear accountability and consistent monitoring across all areas of risk.
Translating Strategy into Measurable Outcomes
One engagement highlights how this approach changes outcomes. A growing organization experienced financial loss due to vendor fraud despite having multiple security tools in place. The issue was not a lack of investment but a lack of governance and structured risk management.
Topor Security conducted a detailed assessment and introduced vendor oversight controls, strengthened email protections and formalized incident response processes. Executive reporting was also implemented to provide visibility into risk metrics.
These changes reduced high-risk vulnerabilities, improved fraud prevention and established accountability across the organization. Leadership gained a clear view of cyber exposure and the ability to make decisions based on measurable data rather than assumptions.
Cybersecurity expectations continue to evolve as organizations adopt new technologies and expand third-party ecosystems. Topor Security continues to focus on governance models, vendor risk methodologies and executive reporting frameworks. By emphasizing visibility, structured decision-making and measurable progress, it enables organizations to manage cybersecurity as a business function aligned with long-term risk management objectives.
