


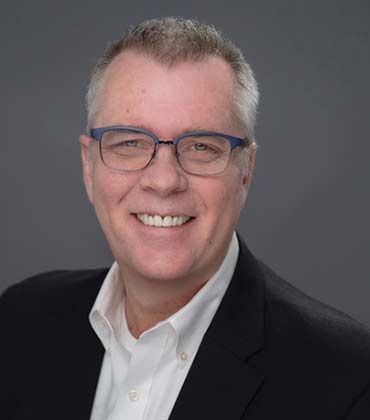
 Jim Edwards, Senior Director of Engineering - PAM
Each identity can hold credentials and potentially access sensitive systems. That makes identity security harder to govern as access moves across endpoints, secrets, services, cloud infrastructure and data, often through tools that operate independently. Any missed or misconfigured controls create gaps in visibility, privilege management and accountability.
Keeper Security addresses those problems by applying the same access controls and governance framework across human, machine, service and AI identities. Its unified platform brings together privileged access management (PAM), secrets management, privileged session management, endpoint controls and AI-powered threat detection, helping organizations enforce least privilege for human and non-human identities alike.
Trusted by more than 100,000 business customers globally, Keeper gives organizations a single way to govern what an identity can access, what privileges it receives and how long that access remains. That level of control becomes critical when the credential itself is legitimate.
“Most breaches no longer start with a broken lock; they start with a valid key in the wrong hands,” says Jim Edwards, Senior Director of Engineering – PAM at Keeper Security. “The moment an attacker uses a stolen credential, they don’t have to break in. They’re already inside. With Keeper, high-security environments gain tighter control over who and what can access critical systems.”
Control That Follows the Identity
Keeper’s principle for privileged access is straightforward: a credential should never be trusted simply because it is valid. It should be trusted only for the specific action it is allowed to perform.
Enforcing that principle becomes harder as identity changes form. An employee may request access from a laptop. A service account may call an application. An AI agent may appear for a single task, retrieve a secret, reach sensitive data and vanish moments later. These identities move through different systems, but Keeper applies the same question to each one: What should this identity be allowed to access right now?
Zero-knowledge and zero-trust architecture set the boundaries. Zero-knowledge keeps customer data encrypted at the endpoint, preventing Keeper or infrastructure providers from accessing plaintext. Zero trust governs what follows. A valid identity does not receive broad entry into the environment. Permission stays limited to a specific resource, task and time window.
“We’re no longer in the day where you can give broad access,” says Edwards. “It has to be granular access.”
Just-in-time permissions grant privilege only when required, while credentials remain hidden from the person, machine or AI agent using them. In many cases, the identity never needs to know the credential at all; Keeper can establish access to an approved resource and remove it once the task is complete.
-
Most breaches no longer start with a broken lock; they start with a valid key in the wrong hands.
That becomes especially important for non-human identities. Machine identities already outnumber human identities, and agentic AI introduces another class that is short-lived and highly active, with implementations exploding across enterprise environments.
“An AI agent should be treated as a privileged user whenever it can access sensitive information,” Edwards says. “Privilege doesn’t just mean something running as an administrator. If an identity has access to sensitive data, that access itself is privileged.”
Keeper applies policy before the agent acts, provides secrets only when needed and uses ephemeral or just-in-time access so privilege does not outlive the task. The same control model follows a human, machine or AI identity from its first request to the resource it reaches.
That continuity is the point. Zero knowledge limits the exposure of sensitive information. Zero trust limits the reach of the identity requesting it. Together, they keep access narrow even as identity becomes faster, more temporary and less human.
When A Valid Credential Becomes The Breach
A stolen credential becomes dangerous because of the unrestricted access it provides once it is accepted.
Before signing on with Keeper, one of the company’s customers learned this during a major breach involving intellectual-property leakage. Its remote-access model relied heavily on a VPN. Once a credential was compromised, attackers opened broad access inside the environment and created room for lateral movement.
Keeper changed that access pattern by securing the organization’s credentials, controlling remote sessions and limiting access to only the necessary resources rather than the wider network. The person or identity initiating a connection does not need to know the underlying credential. Keeper establishes the session, restricts what an identity can reach and closes access once the task has ended.
The result reduces the value of a stolen credential by limiting where it can go.
“PAM has to go beyond vaulting secrets and credentials,” adds Edwards. “It has to control access at a granular level and prevent that lateral movement.”
Consistent Controls, Whatever The Regulator
Highly regulated sectors require controls that are documented, repeatable and defensible when auditors, regulators or customers ask how access is governed.
Keeper applies the same control framework across industries. A federal agency operating under FedRAMP and a hospital subject to HIPAA can use the same core platform, with controls mapped to the framework governing each environment, rather than being rebuilt from scratch. This gives customers a consistent way to enforce policy while meeting sector-specific requirements.
Keeper backs that model with FedRAMP High certification and GovRAMP High authorization, ISO 27001, 27017 and 27018 certification, SOC 2 compliance, FIPS 140-3 validation and PCI DSS Level 1 standing.
“It’s not just a point in time,” says Edwards. “These certifications are part of our DNA because they reflect security best practices every organization can benefit from.”
Beyond Visibility To Control
As human, machine and AI identities move across the same infrastructure, isolated controls become harder to defend. Knowing where an identity went is no longer enough information for a security team. Organizations need policies and controls to follow the identity from its first access request to the resource it ultimately reaches.
“The day of point solutions for each portion of the information chain is kind of gone,” says Edwards. “You really need to have that consistent view and security around an identity from end to end.”
For Keeper, identity security no longer ends when access is granted. Access governance continues through every privilege, connection and resource that follows.
